
AI Strategy & Compliance
GDPR-compliant AI for businesses: 4 legal requirements that matter
Most businesses have moved past the question of whether to use generative AI. The open question is how to use it without creating new data protection risks.
That is what GDPR-compliant AI is about. If you are still comparing tools, our overview of the top AI platforms for companies helps you sort the market. This page covers the legal side.
Typical questions when you introduce generative AI in your organization: Who is liable for AI-generated answers? Is the use of AI tools GDPR compliant? Are the AI models trained with our data? Where is our data processed and stored?
What is GDPR-compliant AI?
GDPR-compliant AI means an AI system that processes personal data only on a valid legal basis, for a defined purpose and to the minimum extent necessary, with a data processing agreement in place, documented technical and organizational measures and working processes for data subject rights. Hosting in the EU helps, but it is not enough on its own. What counts is the full setup: contract, architecture, access rights and documentation.
The quickest test: Does the provider sign a data processing agreement (DPA)? Is your data used as training data for its language models? Where is the data center, and which law applies to the provider? You will find the full checklist further down this page.
Earlier articles covered use cases and the technical implementation of generative AI without going deep into the legal aspect. This article is explicitly about the legal framework for artificial intelligence. First, a short definition of the GDPR.
What is the GDPR and why does it matter for AI?
The General Data Protection Regulation (GDPR) ensures that the personal data and privacy of individuals are adequately protected. As data protection is a fundamental right, the GDPR protects the personal data of people in the European Union. At the same time, it strengthens the trust of users and customers.
Although the GDPR is an EU regulation, it has a global reach and is seen as a role model by other countries. It can also apply to providers outside the EU, for example when they offer services to people in the EU. Those who implement the GDPR professionally take measures to ensure data security and prevent misuse. Mandatory documentation of data processing, for example in the records of processing activities, creates transparency and gives data subjects the opportunity to find out how their data is handled.
Opportunities
- More efficiency and productivity
- Time savings
- Better knowledge management
Risks
- Data security and data protection
- Misinformation
- Plagiarism and copyright issues
- Ethical questions
Generative AI offers clear opportunities, but it also brings risks. The goal of the legal and technical design is simple. Get as much value from AI as possible while keeping these risks low.
4 legal requirements for the use of generative AI
The legal requirements for generative AI relate to data processing, data protection, data security, privacy, liability risks and, since 2024, the EU AI Act.
1. Data processing and data protection
- Generative AI often works with large amounts of data. In practice, it is hardly possible to filter out all personal data such as email addresses, phone numbers or names. When you use generative AI, check to what extent the transfer of this data is necessary or can be avoided. This is the principle of data minimization.
- If the input of personal data cannot be avoided, it must be done in compliance with the GDPR. Only then is personal data used in a legally compliant manner. The principle of purpose limitation applies as well: data collected for one purpose cannot simply be reused for another.
- Customers, suppliers and employees have a right to information about how their data is processed. Handle this transparently and select trustworthy AI solutions. At the very least, mention the use of AI in your privacy policy.
- You need the correct legal basis (Art. 6 GDPR), for example consent or a legitimate interest. When a company introduces an AI solution centrally, it documents the legal basis for the company as a whole instead of collecting individual consent for each tool. In addition, the company concludes a data processing agreement (DPA) with the AI provider under Art. 28 GDPR. It covers subcontractors, technical and organizational measures (TOMs) and other points that protect your data.
2. Data security and privacy
- The TOMs and the list of subcontractors are part of the data protection documentation. They show how the AI provider implements the GDPR requirements. Typical topics are access restrictions and controls, encryption, logging and privacy by design.
- Access rights are a data protection topic as well. If an AI assistant can read every document in the company, it can also show salary data or customer records to people who should never see them. GDPR-compliant AI therefore respects existing permissions.
- If you use AI yourself, check whether a data protection impact assessment (DPIA) under Art. 35 GDPR is required. A DPIA is mandatory when processing is likely to result in a high risk to the rights and freedoms of natural persons. Involve your data protection officer early.
3. Liability risks
One of the biggest points of discussion when using generative AI in businesses is liability. For example: who is liable if wrong decisions are made on the basis of AI output?
In individual cases, the company using AI can be held liable. This can concern product liability, contractual liability or data protection. Liability issues often arise from blind trust in the AI output or a lack of review.
Website chatbots, for example, speak on behalf of the company and can make warranty promises or describe features out of context.
If employees have the answer to a customer inquiry generated by AI and send it without checking it carefully, both the company and the employee may be liable. Train your users accordingly. Where decisions with legal or similarly significant effects on people are made purely automatically, Art. 22 GDPR sets additional limits on automated decision making. Keep a human in the loop for such decisions.
For context: violations of data protection rules can lead to fines of up to EUR 20 million or 4% of worldwide annual turnover, whichever is higher. This makes a sustainable AI strategy all the more important.
To minimize liability risks, act proactively. Review your AI systems continuously, keep audit trails that show which sources an answer was based on, and set up regular compliance monitoring for all AI systems in use.
You want to introduce AI in your company?
4. The EU AI Act
The EU AI Act entered into force on August 1, 2024. It sets rules for the development and use of artificial intelligence in the EU, with the aim of ensuring safe and trustworthy AI systems. Its obligations apply in stages: the bans on prohibited practices and the AI literacy requirement have applied since February 2025, and further obligations follow step by step.
At its core, the AI Act divides AI applications into risk classes, from which the requirements are derived:
- Unacceptable risk
- Prohibited, for example social scoring.
- High risk
- Strict requirements, for example for AI used in recruiting, credit scoring or critical infrastructure.
- Limited risk
- Transparency obligations, for example people must know when they are interacting with a chatbot.
- Minimal risk
- No specific obligations, for example spam filters.
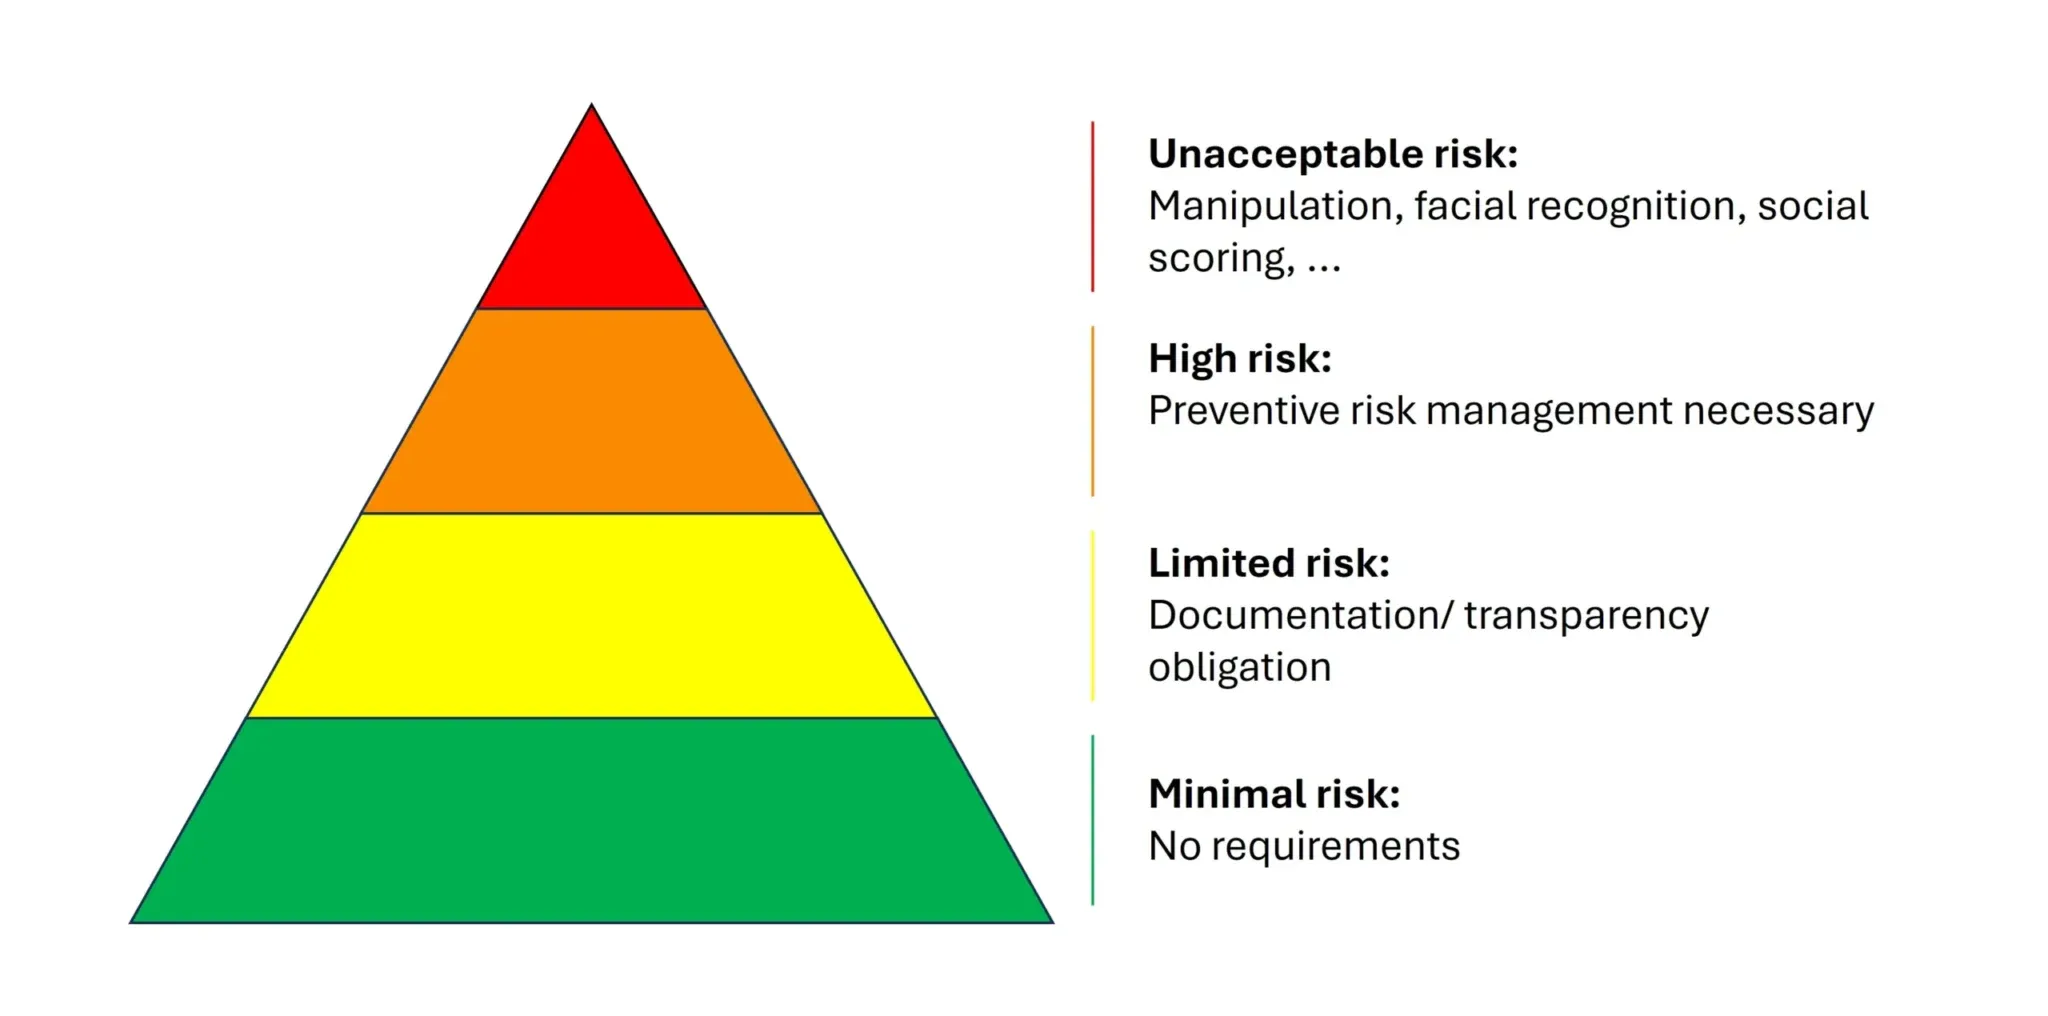
Depending on the classification, the hurdles for introducing AI vary. The AI Act affects both providers that develop AI and organizations that deploy AI internally or offer it to their customers. An internal AI search or knowledge assistant is not listed as high risk per se. This can change if you use it, for example, to evaluate employees. So check every use case.
The AI Act does not replace the GDPR. As soon as personal data is processed, the GDPR applies in addition. GDPR and AI Act compliance therefore belong in one process, not in two separate projects.
To avoid slowing down innovation in the EU, the AI Act combines innovation and safety. The recommendations for users are:
- Assess your AI application according to risk class
- Follow best practices
- Document for traceability
- Train and sensitize your employees (AI literacy)
- Keep an eye on legislative changes and the implementation timeline
GDPR-compliant AI checklist: 10 points before you roll out an AI tool
- 01
Point 1
Use case and legal basis
Define the use case and document the legal basis for each processing purpose.
- 02
Point 2
Data processing agreement
Sign a DPA under Art. 28 GDPR with your AI provider (a key compliance document) and check the list of subprocessors.
- 03
Point 3
Records of processing
Add the AI tool to your records of processing activities (Art. 30 GDPR).
- 04
Point 4
DPIA
Check whether a data protection impact assessment is required and document the result.
- 05
Point 5
Data residency
Know where your data is stored and processed, and which legal system applies to the data center and the provider.
- 06
Point 6
Third-country transfers
For transfers outside the EU, check whether an adequacy decision exists or whether you need standard contractual clauses plus a transfer impact assessment. Assess the CLOUD Act exposure of US providers.
- 07
Point 7
Training data
Make sure the contract excludes the use of your inputs and documents as training data for AI systems of the provider.
- 08
Point 8
Access rights
The AI must respect existing permissions, so that user data and customer data only reach authorized people.
- 09
Point 9
Data minimization and purpose limitation
Connect only the data sources the use case needs and define deletion periods.
- 10
Point 10
Transparency and data subject rights
Update your privacy policy, define processes for access and deletion requests and keep audit trails.
Involve your data protection officer and IT security early. This checklist is not legal advice. It helps you structure the conversation with them. And GDPR compliance is not a one-off project: compliance monitoring continues as long as the AI systems run and new data sources are connected.
How can business AI be made available to employees in a GDPR-compliant way?
In principle, there are various technical ways to make AI available to employees, for example:
- A public AI model
- Your own AI model
- AI integrated into existing software
- AI assistants and AI platforms
- AI agents or generative AI search
- Direct access to language models via an AI API
Each option can be set up in different ways. The graphic shows possible set-ups schematically with examples.
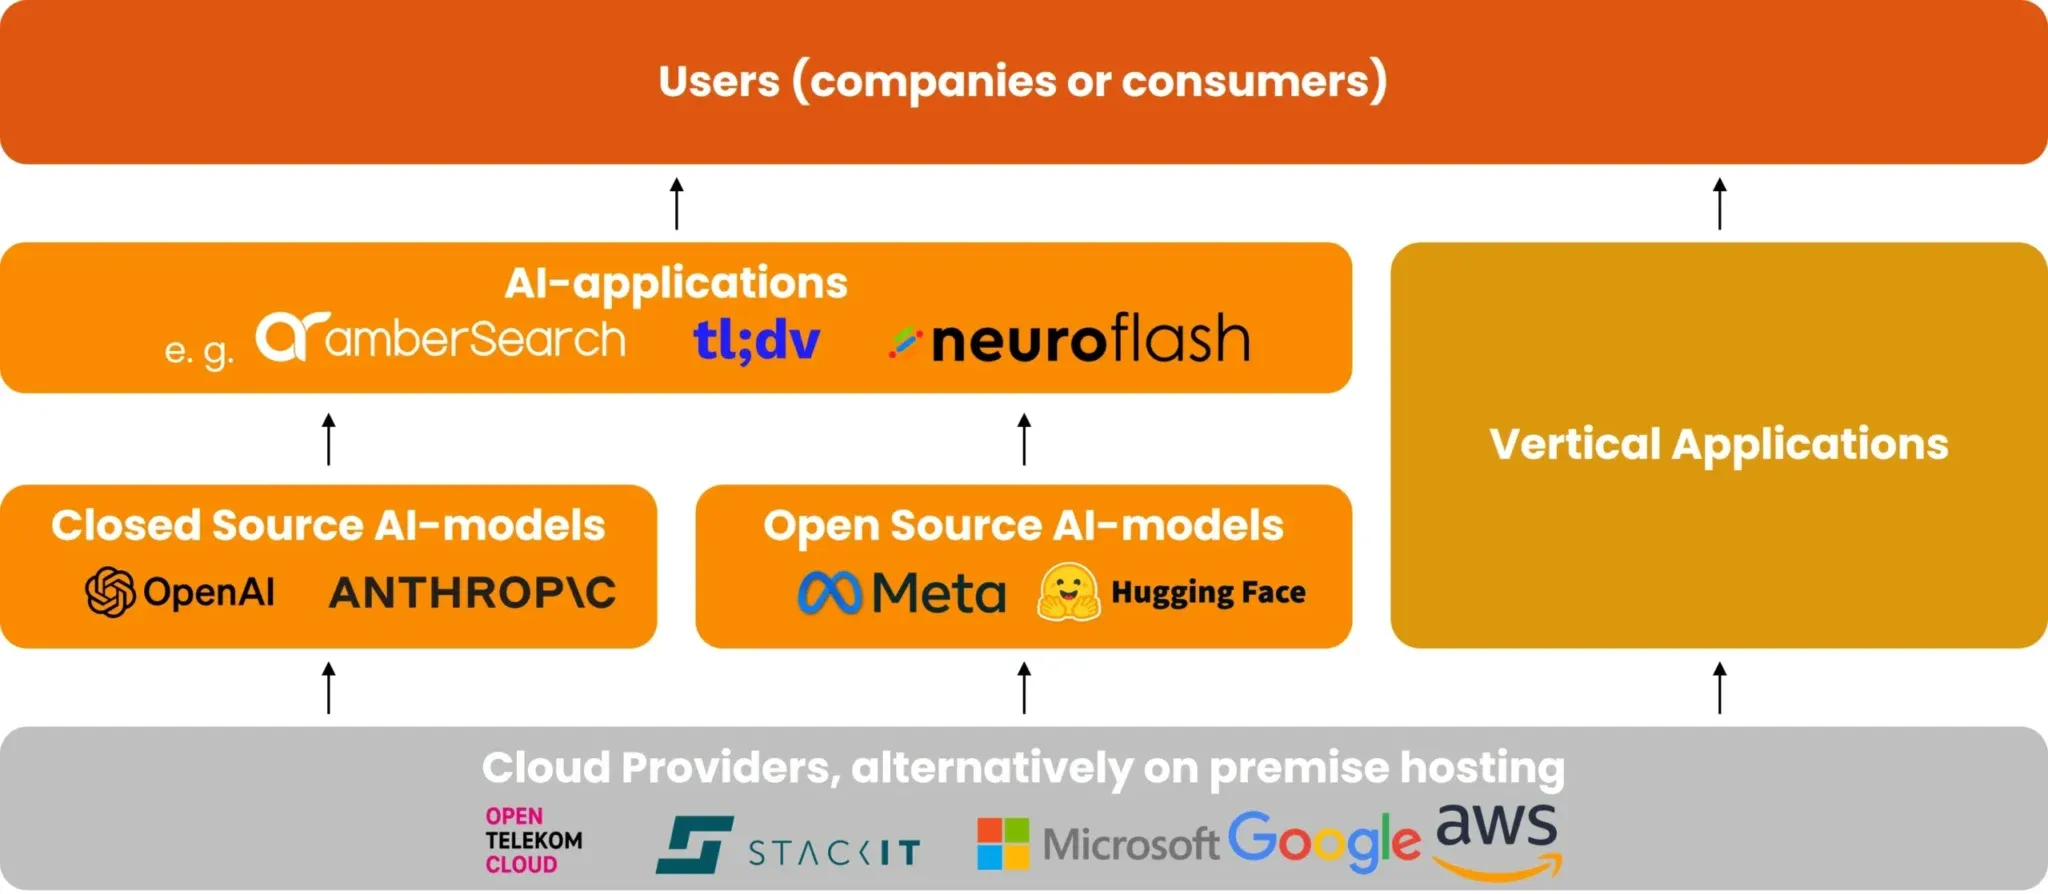
For most businesses, hosting on their own servers does not pay off. The hardware alone, without installation, costs a mid five-figure sum or more, which rarely allows a positive business case, especially for SMEs. That is why most organizations use hyperscalers or cloud providers, either as a private cloud or managed by the AI provider as classic cloud hosting. This article compares cloud vs. on-premise hosting options. The same rules apply if you connect a model via API for AI processing: DPA, data location and no training on your data.
Data storage and processing in the EU
Data storage and processing in the EU still requires GDPR-compliant processing. Internal guidelines define how personal data is handled in AI systems. The lawfulness of data processing must be guaranteed: a suitable legal basis, such as consent or a legitimate interest, plus the corresponding data protection agreements. As it is often difficult to obtain separate consent in practice, take the following measures:
- Conclude a data processing agreement (DPA) with the AI provider.
- Mention the provider in the privacy policy and document it in the records of processing activities, including subcontractors.
- Document which data is entered and connected.
- Review and, if necessary, adapt the technical and organizational measures.
- Train users regularly.
- Ensure data subject rights through suitable processes.
Data processing and storage in the US: Data Privacy Framework and CLOUD Act
Under the EU-US Data Privacy Framework, certified US companies can receive personal data from the EU on the basis of an adequacy decision of the European Commission. However, this adequacy decision can be challenged in court. Its predecessors, Safe Harbor and Privacy Shield, were both declared invalid by the Court of Justice of the European Union. If that happens again, your investment in a tool can become hard to use from one day to the next.
There is a second point. The US CLOUD Act allows US authorities to request data from US providers, even if the data is stored in an EU data center. EU hosting by a US provider is therefore not the same as European data sovereignty. Especially in geopolitically uncertain times, more and more businesses opt for sovereign solutions from Germany or the EU. This gives them more control over their data under European law.
On-premise solutions: processing on your own servers
Many of the challenges mentioned (for example the DPA and the TOMs of an external provider) do not apply to on-premise solutions, as the company is then responsible for hosting the AI software itself. The GDPR still applies to your own processing. However, these systems require a lot of hardware and expertise. In addition, AI solutions must be continuously developed, and hardware requirements change with larger models.
How amber handles GDPR compliance
This is how we put these requirements into practice at amber. Since 2020, we have been developing amber in Aachen: a European business AI platform that brings together knowledge from over 70 data sources and makes it usable through amber (search), amberAI (chat), amberAgents (agents) and amberProjects (projects).
For us, two things are particularly important: existing access rights and GDPR compliance. That is why we follow a trusted partner strategy and only host where European law applies.
FAQ: GDPR and AI in practice
Is ChatGPT Business GDPR compliant?
It can be used in a GDPR-compliant way, depending on the setup. Compliance is not a product feature: what matters is how you configure and use the tool. For any business plan, check whether the provider signs a DPA, excludes your data from model training, where the data is processed and whether the CLOUD Act applies. Then document the result in your records of processing and, if needed, in a DPIA.
How is AI regulated under GDPR?
The GDPR does not contain a separate chapter on AI. It applies to AI wherever personal data is processed: legal basis, purpose limitation, data minimization, transparency, data subject rights, security and limits on automated decision making. The EU AI Act adds AI-specific rules on top.
What does it mean to be GDPR compliant?
GDPR compliance means that you process personal data lawfully, transparently and securely, and that you can prove it. For AI, this means a valid legal basis, a DPA with the provider, documented TOMs, an entry in the records of processing and working processes for data subject requests.
Do you need a data protection impact assessment for AI?
Not for every use case. A DPIA under Art. 35 GDPR is required when processing is likely to result in a high risk for the people concerned, for example with large volumes of sensitive data or systematic evaluation of people. The use of new technologies such as AI is one of the factors that point toward a DPIA. Check it with your data protection officer and document the decision either way.
What is the difference between the GDPR and the AI Act?
The GDPR protects personal data, no matter which technology processes it. The AI Act regulates AI systems themselves according to their risk, even if no personal data is involved. In practice, most business AI projects have to meet both.
Who is liable for AI-generated answers?
In most cases, the responsibility lies with the company that uses the AI output, and with the people who act on it without checking. That is why review processes, user training and clear rules for customer-facing use belong in every AI rollout.